Key Takeaways
- Governance is the operating infrastructure that determines whether CX outsourcing protects your brand and customers or quietly erodes both.
- The main failure points in SMB CX BPO relationships are structural unclear decision rights, weak escalation paths, and governance that exists only on paper.
- A practical SMB governance model can be built around four elements roles and ownership, a focused metric set, a predictable communication rhythm, and lightweight change and risk management.
- Governance must be right sized for a 10 to 100 agent environment and designed to run with a lean internal team, not copied from an enterprise template.
- Strong governance turns a CX BPO from a transactional vendor into a true operating partner and is the only way to manage risk, compliance, and ROI responsibly at scale.
Article at a Glance
When an SMB hands thousands of customer interactions to an offshore CX BPO partner, the contract is not what protects the business. The governance model is. The organizations that see stable performance from outsourcing are not those with the most polished SOW, but those that treat governance as part of the system design, not as a status meeting.
This article lays out a practical governance blueprint for SMBs running 10 to 100 agents through a CX BPO partner, often offshore in the Philippines. It explains why traditional vendor management falls short, how to structure governance across strategic, operational, and tactical layers, and how to implement a four element framework that fits a lean team.
You will find specific role maps, meeting rhythms, example scorecards, change classification guides, and composite scenarios from retail, regulated services, and subscription businesses. The goal is not theory. The goal is a structure you can realistically run, month after month, that keeps your CX outsourcing relationship aligned with your customers, your brand, and your risk boundaries.
Why Governance Is Now a Leadership Priority in CX Outsourcing
Governance structures for SMBs working with CX BPO partners are not optional overhead. They are the operating system that determines whether outsourcing delivers on its promise or slowly undermines customer trust.
The shift from viewing BPO as a pure cost move to treating it as a strategic CX decision has raised the stakes. Offshore teams no longer handle just low risk tickets. They manage billing disputes, sensitive healthcare inquiries, retention conversations, and outage communications where a single mishandled escalation can trigger complaints, churn, or regulatory scrutiny.
Most SMBs still manage these relationships with a contract, a weekly call, and a shared inbox. That worked when external teams handled narrow, repetitive work. It does not work when your partner is effectively running a second contact center site on your behalf.
Without a designed governance model, even a technically strong BPO partner will drift out of alignment with your processes, your risk tolerance, and your customers. The internal team experiences this drift as more escalations, more exceptions, and more time spent interpreting reports that no longer match what leaders see in their own dashboards.
What Governance Really Means in a CX BPO Relationship
Governance in a CX BPO relationship is the operating structure that sits between the contract and the day to day work. It is not a document, and it is not just a set of meetings. It is the combination of decision rights, ownership, reporting, and communication rhythms that let two organizations operate as one system.
The contract defines what the partner is paid to do scope, price, SLAs, data obligations, termination terms. Governance defines how both sides will actually run the relationship how decisions get made, who approves changes, how issues are escalated, and how performance is interpreted rather than just reported.
Governance vs Contract
Many SMBs treat the contract as the governance model. That is where problems start. A contract cannot answer questions like:
- Who approves a process change when a new product launches?
- Who on the BPO side can escalate a compliance sensitive call in the moment?
- What happens when a metric drops below threshold who calls the meeting, and what is the standard response timeline?
When governance is not explicitly designed, both sides fall back to the only shared reference they have the SOW and MSA. Performance conversations turn into contract interpretations, and every issue with a grey area becomes a debate about scope rather than a joint problem solving exercise.
Decision Rights, Accountability, and Communication
Effective governance rests on three pillars that must work together:
- Decision rights Clearly defined authority for script changes, exception handling, staffing adjustments, and risk decisions.
- Accountability Named owners on both sides for relationship health, performance reporting, escalations, compliance coordination, and change management.
- Communication architecture The actual meeting rhythm and escalation channels that keep decisions and ownership from becoming theoretical.
Without explicit decision rights, everything escalates. Without clear owners, everything is “shared” until something goes wrong. Without predictable communication, even good metrics and roles go stale because there is no forum to act on them.
The Three Layers of CX BPO Governance
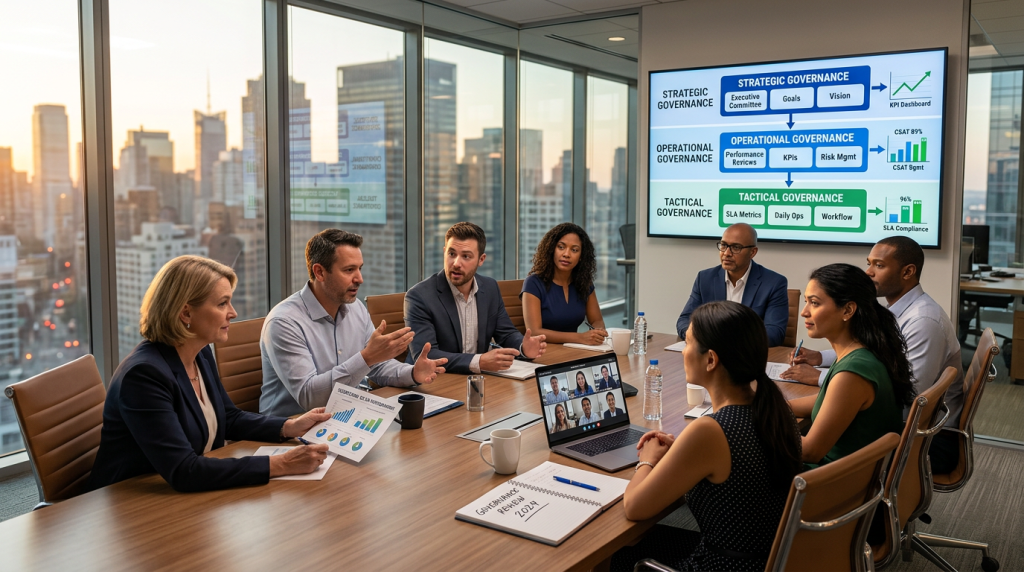
Governance decisions do not all belong in the same room. The questions a COO cares about are not the same as the questions a floor supervisor needs answered in real time. Trying to manage everything through a single weekly call creates congestion and missed signals.
A workable governance model separates conversations into three connected layers.
Strategic Layer Direction, Risk, and Outcomes
This is where senior leaders on both sides align on:
- Business objectives and success criteria for the relationship.
- Risk boundaries around brand, compliance, and customer experience.
- Scope changes, major investments, and long term direction.
Cadence is usually quarterly, with extra sessions during transitions. The focus is not SLA charts; it is whether the relationship still matches what the business needs and whether emerging risks warrant structural changes.
Operational Layer Performance, Process, and Coordination
This is where most governance work happens. Typical agenda:
- Review governing metrics and trends.
- Surface and resolve process gaps.
- Coordinate staffing, queue changes, knowledge base updates, and technology impacts.
Cadence is weekly or bi weekly. Participants are the client CX or operations lead and the BPO operations or account manager. This is the forum that keeps the contract alive as an operating reality instead of a static document.
Tactical Layer Escalations and Frontline Rules
This layer governs decisions that cannot wait for a meeting:
- Which issues must be escalated immediately, and to whom.
- What authority frontline teams have during non overlapping time zones.
- How unanticipated exceptions should be handled.
For offshore teams, this layer is critical. If escalation rules are vague, agents default to “safe but unhelpful” behavior deferring decisions, over escalating, or giving generic answers that frustrate customers and create more work later.
These three layers are not org chart levels. In a lean SMB, the same person might sit in all three. The distinction is about the type of decisions and the rhythm they follow, not job titles.
Why SMBs Struggle to Govern CX BPO Partners
The governance gaps leaders see in CX outsourcing are rarely about intent. They are about structure and capacity.
The Pattern That Repeats
A typical sequence:
- Launch with good intentions a kickoff, a process document, and a weekly call.
- Six months later, the weekly call has turned into a rolling status update.
- The original process document has not been touched since go live.
- The partner is sending performance reports, but the client is not using them to drive decisions.
- No one remembers the last time the escalation path was reviewed or tested.
The relationship is technically “fine” until a peak season, a product launch, or a compliance question exposes that there is no functioning governance model underneath.
Thin Teams and Tribal Knowledge
SMBs run lean. The person “owning” the BPO relationship usually also:
- Manages internal operations.
- Handles higher level escalations.
- Reports to finance and the CEO.
At the same time, many critical processes and exception rules live in a few people’s heads. When those people are unavailable or change roles, the offshore team either improvises or waits. Both outcomes are risky at scale.
Common Governance Failure Patterns
Three patterns show up again and again in SMB CX BPO relationships:
- Contract only governance Performance is managed against the SOW and SLA grid, with little living structure on top. Small misalignments accumulate until they become disputes.
- Single point of knowledge One internal leader carries all the working knowledge and relationship context. When they are out, governance effectively pauses.
- Launch and abandon The relationship gets intense oversight during launch, then the governance structure quietly dissolves once things feel stable. Meetings get shorter and less structured, documentation stops updating, and change communication reverts to ad hoc emails.
Recognizing which pattern you are drifting into is the first step toward redesigning governance before performance suffers.
What Good Governance Looks Like for a 10 to 100 Agent CX BPO
High performing SMB BPO relationships do not mimic enterprise governance. They use a simpler model that still delivers alignment, accountability, visibility, and risk control.
Right Sized Governance
A 10 agent program does not need a steering committee. It needs:
- A named relationship owner on each side.
- A weekly 45 minute operational review with a standing agenda.
- A documented escalation path that every supervisor and team lead knows.
- A quarterly strategic check in with senior leaders on both sides.
As you scale toward 50 or 100 agents, or add more complex interaction types, you add structure where the current model starts to creak more focused reviews, function specific metrics, and more formal steering, not more bureaucracy everywhere.
The main signal that governance needs to evolve is behavioral, not numerical:
- Weekly meetings consistently run out of time.
- Tactical issues crowd out strategic discussion.
- Escalations bypass the documented path because the path is not working.
Three Elements That Matter Most
Across different SMB profiles, three elements separate governed relationships from ones that quietly drift:
- Simple decision rights Who can decide what, at what threshold, without needing a committee.
- Predictable cadences A clear rhythm weekly, monthly, quarterly that people can plan around.
- Clear escalation paths When something breaks, everyone knows the exact sequence and contacts.
When these three exist and are kept current, most other elements can be improved over time. When they are missing, adding more dashboards or more contract detail does not fix the problem.
Core Components of an SMB CX BPO Governance Framework
A workable SMB governance framework does not need exotic structures. It needs a minimum set of components that cover the real failure modes.
Defined Roles and Decision Authority
Every critical function must have a named owner on both sides. At SMB scale, one person can hold multiple roles; the point is explicit ownership, not headcount expansion.
Minimum Role Map
| Function | Client Side Owner | BPO Side Owner | Notes on Authority |
| Relationship management | CX or operations lead | Account manager | Operational decisions, scope recommendations |
| Performance reporting | CX or ops lead | Reporting analyst or ops | Metrics interpretation shared |
| Quality assurance | CX lead or QA contact | QA lead | Calibration joint, scoring run by BPO |
| Escalation handling | Named escalation owner | Team lead or supervisor | Based on escalation matrix |
| Compliance coordination | Legal or IT stakeholder | Compliance liaison | Client side approval for sensitive changes |
| Change management | CX or operations lead | Account manager | Client initiates, BPO implements and confirms |
On the client side, governance has to account for legal and IT involvement where data handling, HIPAA relevant workflows, or other sensitive processes are in play. Those stakeholders may not sit in weekly reviews, but the model must make clear which changes cannot move without their approval.
Governing Metrics and SLA Structure
You do not need 30 metrics in governance. You need a small set that truly reflect performance and risk.
Typical governing metrics in an SMB CX context:
- First contact resolution rate.
- Average handle time against target.
- Customer satisfaction or quality score from surveys or QA.
- Escalation rate to client side or higher levels.
- Schedule adherence or coverage against forecast.
- Repeat contact rate within a defined window.
For regulated or sensitive environments, add at least one compliance adjacent indicator, such as:
- Percentage of interactions flagged for compliance review.
- Adherence to required disclosure language.
The test for a governing metric is simple If it moved significantly, would you change a decision about staffing, process, or scope? If not, it belongs in the BPO’s internal operational reporting, not your governance scorecard.
Communication and Escalation Cadence
A basic cadence that works for most SMBs looks like this:
| Meeting Type | Frequency | Participants | Primary Focus |
| Operational review | Weekly | Client CX lead, BPO ops manager | SLA metrics, open issues, process exceptions |
| Performance deep dive | Monthly | CX or ops lead, finance rep, BPO account | Trends, QA insights, improvement plans |
| Strategic review | Quarterly | Senior leaders on both sides | Relationship health, scope, risk, roadmap |
| Escalation debrief | As needed | Named owners on both sides | Root cause, corrective action, documentation |
The weekly review is the anchor. Data should be reviewed before the call so the time is spent on interpretation and decisions, not on walking through numbers. Each meeting needs:
- A standing agenda.
- A facilitator.
- A shared action log with owners and due dates.
Without those basics, governance meetings quickly degrade into status updates that no one prepares for and everyone de-prioritizes.
Change and Risk Management Protocols
Most misalignment in CX BPO relationships shows up around change. New products, new policies, new offers, seasonal spikes all can create friction if handled informally.
A simple change classification guide keeps the process lightweight but controlled:
| Change Type | Examples | Approval Required From |
| Minor process update | Script wording tweak, FAQ clarification | Client CX lead |
| Moderate process change | New escalation criteria, new offer rules | CX lead and BPO operations manager |
| Significant scope change | New interaction type, major staffing change | Senior client leadership and BPO director |
| Compliance sensitive | Data handling, disclosure language, system access | Client legal or IT and BPO compliance liaison |
Alongside classification, you need minimum documentation for each change:
- What is changing and why.
- Effective date and implementation window.
- Who approved it.
- What training or knowledge base updates are needed.
- How both sides will verify that the change is live and correct.
Compliance sensitive changes must run through the client’s own legal, IT, and compliance processes. A BPO partner can help implement and maintain agreed frameworks, but ownership of regulatory posture remains with the client.
A Practical Four Element Governance Framework for SMB CX BPO
A simple, workable framework for SMBs running a Philippines based CX team in the 10 to 100 agent range can be built around four elements:
- Roles and ownership.
- Metrics and reporting.
- Communication and escalation rhythm.
- Change and risk management.
This framework is designed for leaders who do not have a dedicated vendor management office. It assumes governance is one part of someone’s job, not their entire remit.
Element One Roles and Ownership
The first step is naming who owns what, on both sides. That sounds basic, but most struggling relationships cannot produce a one page contact and ownership map that everyone agrees on.
Practical steps:
- Create a one to two page role map using the table above.
- Make it explicit where one person holds multiple roles and document backups for each critical function.
- Share this map with the BPO partner and confirm their equivalent contacts and availability windows.
The relationship owner on the client side is especially important. Without someone who has real authority and the time to exercise it, the partner ends up waiting on decisions or bouncing between multiple stakeholders with conflicting expectations.
Element Two Metrics, SLAs, and Reporting
Next, define the governing scorecard.
Steps:
- Pick four to seven metrics using the decision relevance test.
- Establish baselines from internal performance or a short pre pilot period.
- Agree on ranges or thresholds that will trigger a governance discussion, not just contractual penalties.
- Build a simple one page view current period, prior period, and a basic trend indicator.
Make sure the client team has direct access to reporting dashboards and call recordings. Leaders should be able to log in, see the same numbers the BPO sees, and listen to a sample of interactions without waiting for someone to pull a report.
If AI assisted QA is in place, use that data to feed the quality score so that it reflects 100 percent of interactions, not a small sample. The governance decisions that follow still belong to human leaders, but the underlying signal becomes more reliable.
Element Three Communication and Escalation Rhythm
Define and protect the basic cadence:
- Weekly operational review 45 to 60 minutes.
- Monthly performance deep dive 60 to 90 minutes.
- Quarterly strategic review 60 to 90 minutes.
For each:
- Lock the time and participants.
- Use a consistent agenda format.
- Track and revisit action items.
Then, define the escalation path so it actually gets used under pressure:
- Limit it to two or three tiers, each with a named contact and expected response time.
- Train supervisors and leads on the criteria for each tier.
- Account for time zones where offshore teams operate outside your core hours by defining which decisions they can make independently at night and which must wait for the overlap window.
An escalation path that only exists in a shared drive is not governance. Supervisors and managers should be able to describe it from memory.
Element Four Change and Risk Management
Finally, put lightweight structure around changes and risk reviews.
For changes:
- Use the classification table to route approvals.
- Maintain a simple change log what changed, who approved it, when it went live.
- Run a quick verification step after each significant change sample calls, targeted QA, or focused metric review.
For risk:
- Use the monthly deep dive to flag metrics moving in concerning directions before they breach thresholds.
- Use the quarterly review to discuss structural risks key person dependencies, data handling gaps, vendor concentration risk, and governance fatigue.
In regulated environments, ensure that any change affecting data flows, access, or regulated language is routed through client legal and IT before it reaches the BPO partner for implementation.
Implementing Governance with a Lean Internal Team
The most common pushback on governance in SMBs is capacity. Leaders are already stretched. The idea of adding more structure can sound like adding more work.
In reality, most lean teams already spend the time. They just spend it reactively, in escalations and ad hoc problem solving, rather than in a predictable rhythm that prevents problems from compounding.
How Much Time Good Governance Actually Takes
For a 10 to 50 agent CX BPO relationship, a realistic monthly time budget for the client side relationship owner is in the range of six to ten hours:
- Weekly operational reviews about three hours per month.
- One monthly deep dive plus scorecard prep around three to four hours.
- Change documentation and coordination one to two hours, depending on activity.
- Quarterly strategic review prep amortized is minimal.
That is roughly five to six percent of one full time role. For a relationship handling thousands of customer interactions, that is a reasonable investment to avoid fire drills, misalignment, and preventable risk.
Fitting Governance into Existing Roles
To make this sustainable:
- Map governance responsibilities onto existing functions instead of inventing new roles. The person who owns CX reporting internally should own performance reporting governance. The IT lead who manages external access should own technical and access related approvals.
- Keep documentation light and practical. A two page operating guide beats a 30 page governance charter that no one uses.
- Use a single shared “relationship operating guide” as the source of truth for roles, scorecard, escalation path, and change protocol. Update that document as things evolve instead of scattering information across email threads and slide decks.
Governance should feel like a cleaner way of doing work you already do, not a parallel universe of extra meetings and documents.
Governance Across the Lifecycle Pilot, Stabilization, and Scale
Governance needs change as the relationship moves from pilot to steady state to multi function or higher volume scale. Keeping the same model through all three stages either under controls risk or overburdens the team.
Pilot Phase Learning and Decision
In a pilot, governance priority is learning and clear go or no go decisions, not perfection.
Pilot governance should include:
- All four core artifacts role map, scorecard, escalation path, and change protocol even if simplified.
- Explicit pilot goals what questions you want answered beyond “does it work.”
- Clear decision criteria for what constitutes a successful pilot, agreed before launch.
- Midpoint and end of pilot reviews that are documented and involve senior leadership.
If those elements are missing, the pilot will produce data but not clarity. You end up with opinions instead of a shared decision.
Stabilization Phase Consistency and Documentation
After a successful pilot and early ramp, the focus shifts to making the model sustainable:
- Formalize processes that worked during the pilot.
- Refine exception handling based on what actually occurred.
- Validate that the governing metrics truly predict the outcomes you care about.
- Adjust meeting frequency down to a sustainable rhythm once the operation is stable.
This phase usually takes two to four months. Skipping it and jumping straight from pilot intensity to “set and forget” is one of the fastest paths to launch and abandon governance.
Scale Phase Coordination and Resilience
As the relationship grows in agent count, interaction types, or geographies, governance must keep pace:
- Separate metrics and reviews by function instead of averaging everything into one scorecard.
- Distribute relationship ownership across more than one internal leader to avoid single owner bottlenecks.
- Introduce a simple steering forum when the relationship crosses thresholds in size, complexity, or regulatory impact.
Signals that your model has fallen behind:
- A single weekly meeting cannot handle the agenda.
- One relationship owner becomes a bottleneck for approvals.
- Escalations and changes for different processes all flow through the same people, stretching response times.
Scaling governance is not about more meetings. It is about better separation of concerns so that each layer can do its job without clogging another.
Scenarios Where Governance Makes or Breaks the Relationship
The same structural ideas play out differently in different SMB contexts. The following composite scenarios illustrate typical tradeoffs and responses.
Scenario One Lean Retail CX Team with Seasonal Peaks
A specialty retailer runs a lean four person internal CX team and uses a Philippines based BPO partner for 25 agents, ramping to 45 during holiday peaks. The first year goes reasonably well, but peak season feels chaotic every time. Escalations spike, and post season reviews are full of “we should have” insights that never seem to stick.
A governance review surfaces three structural gaps:
- Seasonal ramps are handled informally through emails and last minute briefings instead of a defined seasonal readiness plan.
- The escalation path is not updated for peak conditions, so high priority issues compete with normal volume.
- There is no post peak governance review on the calendar, so lessons from one season do not systematically feed the next.
The retailer and BPO partner respond by adding a seasonal checklist to the quarterly governance calendar, updating the escalation path 30 days before the ramp, and scheduling a dedicated post peak debrief. No new headcount, just more deliberate governance around predictable events.
Scenario Two Regulated Services Firm with Compliance Sensitive CX
A regional insurance brokerage outsources first contact customer service policy questions, billing, and scheduling to a 30 agent offshore team. Legal and compliance stakeholders review the contract but have no ongoing role in governance.
A routine audit discovers that script language for a specific coverage inquiry has drifted from the approved version. The cause is not malice. Over time, minor verbal updates and local clarifications were passed along without formal review, and there was no category in the change protocol that forced those updates back through legal.
The fix is structural:
- Add a compliance sensitive change category that includes any customer facing language about coverage, obligations, or regulated disclosures.
- Require legal sign off for that category, while leaving other process changes in a faster approval path.
- Add a brief compliance review to the quarterly strategic governance meeting so legal can see emerging patterns without sitting in weekly ops calls.
Compliance remains the client’s responsibility. Governance ensures there is a clear route for compliance relevant changes and that the BPO partner is not left to interpret legal boundaries on its own.
Scenario Three Growing Subscription Business Expanding Scope
A subscription software company starts with a 12 agent pilot focused on tier one support. Over 18 months, the relationship expands to 55 agents across tier one, billing, and retention functions. Governance, however, has not changed since the 12 agent pilot.
Symptoms:
- A single client relationship owner is overloaded and slow to respond.
- Performance metrics are blended across all functions, masking issues in specific areas.
- The same weekly meeting tries to cover three different queues, creating shallow conversations.
A joint governance diagnostic maps current practices against the four element framework and exposes structural gaps. The governance redesign:
- Splits the scorecard into function specific views with distinct owners.
- Assigns a second internal lead for billing and retention, with clear division of accountability.
- Introduces brief function specific operational reviews while maintaining a cross functional weekly leadership sync.
- Formalizes change paths by function so that a billing update does not go through the same approval route as a technical support script change.
Again, no extra headcount. Just governance brought back into alignment with the current scale and complexity of the relationship.
Frequently Asked Questions from SMB Leaders About CX BPO Governance
What is the minimum governance structure an SMB needs with a new CX BPO partner?
At a minimum, you need:
- A named relationship owner and escalation contact on both sides.
- A small governing scorecard with four to seven metrics and agreed thresholds.
- A documented escalation path with criteria, contacts, and response expectations.
- A simple change protocol describing how process updates are approved and communicated.
Without those four, you do not have governance; you have a contract and a vendor.
How often should governance and operational reviews happen?
Weekly operational reviews and monthly deep dives are a solid baseline. During pilots and major transitions, you may need more frequent touchpoints. Once the relationship is stable and predictable, some teams shift weekly reviews to bi weekly, but that should be a conscious decision based on performance and risk, not a gradual slide driven by calendar pressure.
Quarterly strategic reviews are the minimum cadence for senior level oversight. They ensure relationship health and risk discussions do not get crowded out by day to day firefighting.
Which metrics matter most for governance versus day to day operations?
Governance metrics are the small set that directly influence business decisions. They typically cover:
- Quality or customer satisfaction.
- First contact resolution and repeat contacts.
- Escalation rate.
- Handle time vs target and schedule adherence.
- Any key compliance or risk indicators.
Operational metrics such as queue wait times, per agent adherence, and detailed contact reasons belong in the BPO’s internal management layer unless a specific issue elevates them to the governance agenda.
Can a small internal team realistically manage BPO governance without dedicated vendor managers?
Yes, as long as the governance model is designed for the team you actually have. That means:
- Assigning governance responsibilities to existing roles that already touch CX, finance, IT, and legal.
- Keeping documentation lean and actionable.
- Running a tight meeting rhythm that focuses on decisions, not reports.
What does not work is importing an enterprise style governance framework with elaborate committees and extensive reporting into a five person CX team. Comprehensive governance that collapses within 90 days under real workloads is less effective than a lean model you can sustain every month.
How does governance change when working with an offshore CX BPO partner?
Two design constraints become more important:
- Time zones You must define which decisions the offshore team can make autonomously during non overlap hours and which must wait. Without that boundary, agents will either over escalate or under act.
- Documentation and async communication Offshore governance relies more on written processes, consistent ticket notes, and shared logs than on hallway conversations or on the spot clarifications.
Handled well, this discipline improves process clarity and traceability across your entire operation, not just in the outsourced portion.
When should leaders re think or re design their governance model?
Treat any significant change as a trigger, including:
- Agent count increasing by 25 percent or more.
- Adding a new interaction type, function, or channel.
- A key person leaving or changing roles on either side.
- A new regulatory requirement that touches customer contact.
- A sustained performance trend you cannot explain with existing reporting.
- A relationship owner spending more time reacting to issues than working through your governance cadence.
Waiting until a visible failure forces a redesign is more expensive and more disruptive than scheduling a governance review when the early signals appear.
Turning Governance into a Strategic Advantage
Well designed governance is the difference between a CX BPO that adds constant work to your plate and one that extends your capacity without increasing your risk. It is not there to satisfy a box on a procurement checklist. It is the mechanism that keeps your promises to customers, regulators, and your own leadership as the relationship scales.
If your current or planned CX outsourcing setup feels heavier than it should, the next practical step is not another report or another ad hoc escalation. It is a focused governance design session where you map roles, metrics, cadences, and change protocols to the realities of your team and your risk profile.
Start by pressure testing your own structure against the four elements and the scenarios described here. Identify where decision rights are unclear, where metrics do not truly drive decisions, where meetings lack teeth, and where change flows through inboxes instead of a defined path. Those are the highest leverage redesign points.
When you are ready to go deeper, consider a structured conversation with a partner that treats governance as part of the service, not an afterthought. A governance first assessment of your CX outsourcing plan can help you:
- Stress test your current model against real world volume, risk, and compliance scenarios.
- Design or refine a lean governance framework tailored to your technology stack, customer journeys, and team capacity.
If you want to explore how a compliance aware, governance led CX BPO model could work for your environment, reach out to schedule a compatibility and governance design session. You can walk through your current structure, your constraints, and your goals, and leave with a concrete outline for how to govern an offshore CX partnership responsibly from day one.
Disclaimer
Any claims in this article are based on previous experiences with clients and differ from client to client. Optimize CEC cannot make a guarantee on results because they depend on factors including internal processes, organizational readiness, and execution quality.